

 Share on media
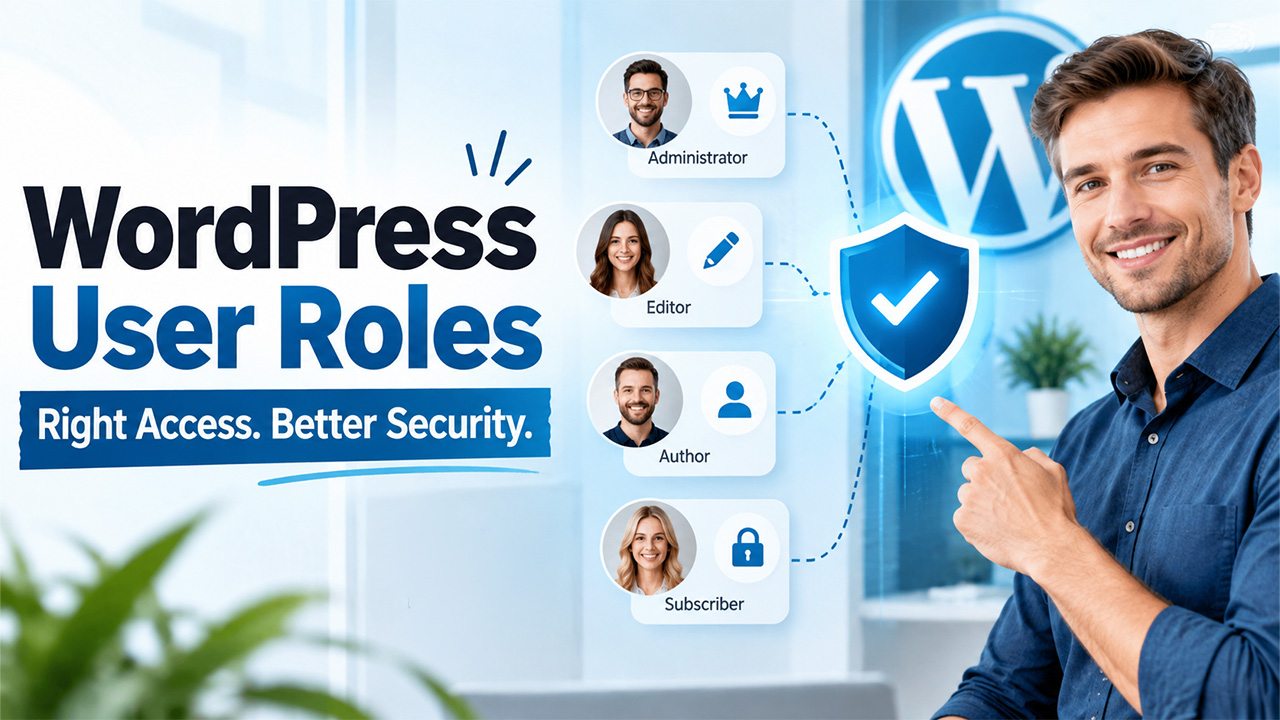


One very important aspect that most visitors of a WordPress site do not take into consideration is user capability and roles. If you run a personal blog, business site, or an e-commerce site, understanding how WordPress handles user access will protect you against security breaches, workflow confusion, and unwanted modifications to your site.
In this article, we will go over all that you need to know regarding user roles, capabilities and how to best use them effectively using WordPress. Whether you are running a personal blog, a company website, or an e-commerce site, knowing WordPress approach to user access can prevent security vulnerabilities, workflow confusion, and unwanted alterations on your site.
For readers who are new to WordPress and want to grasp the fundamentals before diving deeper into roles, see this Website Optimization Guide.
What Are WordPress User Roles?
WordPress user roles define what actions a person can and cannot perform on your site. These actions are called capabilities. For example:
- Writing posts
- Editing posts
- Publishing content
- Managing plugins and themes
- Moderating comments

When you apply a role to a user, you’re really instructing WordPress what they can do. This organization gives you control and ensures your site is secure and efficiently managed.
The Default WordPress User Roles
WordPress has six default roles straight out of the box. Each one has its set of permissions that can’t be modified without going through plugins or custom coding. Let’s dissect them:
1. Administrator
- The most powerful role.
- Full control over the website.
- Can install plugins, edit themes, add users, and delete content.
- Ideal for website owners.
Caution: Never assign this role unless absolutely necessary, as it gives complete access.
2. Editor
- Can create, edit, publish, and delete any posts (their own or others’).
- Can manage comments and categories.
- Cannot access plugins, themes, or user management.
- Best for content managers.
3. Author
- Can write, edit, and publish their own posts.
- Cannot edit or delete posts by others.
- Limited control over media uploads.
- Great for guest writers or contributors who need autonomy.
4. Contributor
- Can write and edit their own posts but cannot publish.
- Posts must be reviewed by an Editor or Administrator before going live.
- Useful for guest writers under supervision.
5. Subscriber
- The most limited role.
- Can read posts, manage their profile, and leave comments.
- Cannot write posts or access the dashboard deeply.
- Best for community members, readers, or registered customers.
6. Super Admin (Multisite Only)
- Exists only on WordPress Multisite installations.
- Can manage the entire network of sites, including themes, plugins, and user roles across multiple websites.\
WordPress User Roles vs. Capabilities: What’s the Difference?
WordPress user roles and capabilities are related, but they are not the same. A user role is a group of permissions assigned to a specific type of user, while a capability controls an individual action that the user can perform.
For example, an Editor can manage and publish content, while an Administrator has access to much broader website settings. Understanding What is WordPress also makes it easier to see how this permission system helps control access across a website.
As your website grows and different people handle writing, editing, marketing, or development, understanding roles and capabilities helps you provide the right level of access without giving unnecessary control.
Why are user roles crucial?
Security – Restricting user permissions prevents accidental or malicious modification.
Collaboration – Simplifies working together by establishing clearly what can be done by whom.
Efficiency – Avoids clutter and confusion by revealing users only the tools they require.
Professionalism – Allows contributors and editors to concentrate on their duty without stepping into technical domains.
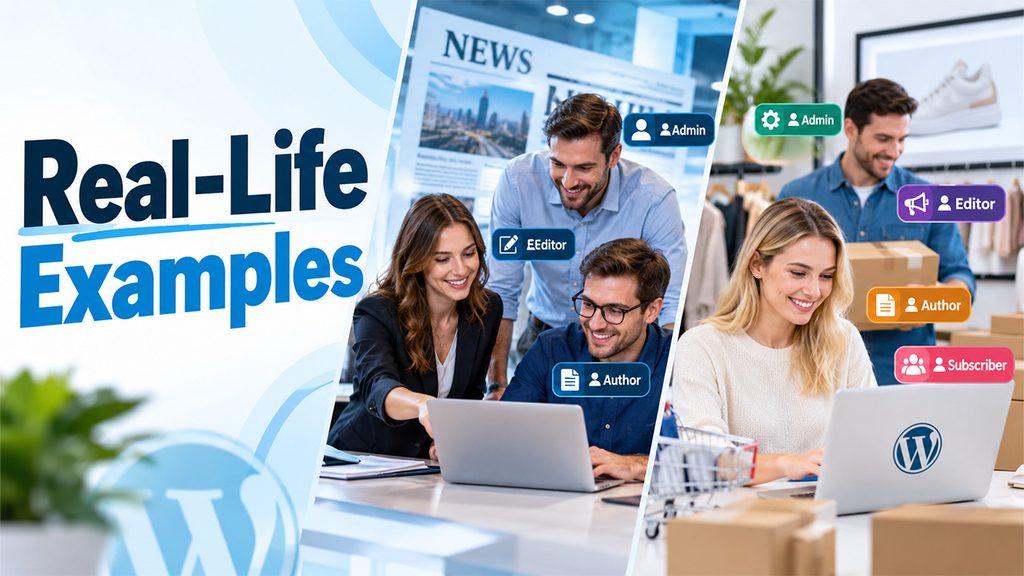
Real-Life Examples
- A news website might assign:
- Administrators → Website owners
- Editors → Senior staff
- Authors → Journalists
- Contributors → Freelancers
- Subscribers → Readers who sign up
- An eCommerce store might use:
- Administrators → Store owners
- Editors → Marketing managers
- Authors → Content creators for product descriptions
- Subscribers → Customers with accounts
Managing User Roles in WordPress
Adding a New User
- Go to your WordPress dashboard.
- Navigate to Users → Add New.
- Fill in details like username, email, and password.
- Assign a role.
Changing User Roles
- Go to Users → All Users.
- Select a user.
- Choose a new role from the dropdown.
- Save changes.
Increasing the Roles of WordPress Users
Sometimes the typical roles just are not enough. You may want a specialised position, such as Support Agent or SEO Manager to handle tasks like performance monitoring and WordPress Maintenance. There are two ways that WordPress allows roles to be expanded and customised:
1. Using Plugins
Some popular plugins are:
Members (by MemberPress) – Create, edit, and remove roles with ease.
User Role Editor – Streamline permissions for any role.
Capability Manager Enhanced – Control capabilities without ever touching code.
These plugins provide you with fine-grained control without having to customize.
2. Custom Code
If you’re comfortable with PHP, you can create custom roles by adding code in your theme’s functions.php file. Example:
<?php

// Add Custom Role

function create_custom_user_role() {

    add_role(

        ' SEO Manager', // role slug (unique ID)

        ' SEO Manager', // role display name

        array(

            'read'          => true,   // can read posts/pages

            'edit_posts'    => true,   // can edit their own posts

            'edit_others_posts' => true, // can edit others' posts

            'publish_posts' => true,   // can publish posts

            'upload_files'  => true,   // can upload media

            'manage_options' => false, // cannot access site settings

        )

    );

}

add_action('init', 'create_custom_user_role');

?>
An SEO Manager role with particular permissions is created as a result.

How to Test Custom User Roles Before Giving Access
Creating a custom role is useful, but it should be tested before assigning it to a real user. Create a temporary account with the new role and check what it can access from the WordPress dashboard.
Test important areas such as posts, pages, media, plugins, and settings. Also confirm that the user cannot access features that are outside their responsibilities.
For websites using multiple tools as part of a broader WordPress and CMS workflow, testing roles can help identify permission conflicts before they affect the live website. A quick review can prevent access problems and make user management safer and more organized.
Best Practices for User Role Management
- Adhere to the Principle of Least Privilege
- Grant permissions to users only what they require, and nothing more.
- Use Plugins for Flexibility
- Rather than editing WordPress core files, use the built-in trust in plugins.
- Periodically Audit User Roles
- Your user list should be reviewed periodically every few months and inactive users be deleted.
- Limit the Number of Administrator Accounts
- If there are a lot of admins, the risks increase, so keep it to a minimum.
- Employ Robust Authentication
- Users should be encouraged to use 2 Factor Authentication (2FA) and create strong passwords.
- Get Your Team Educated
- Educate your users on what their job is, and how to avoid common mistakes.
Common Errors to Steer Clear Of
- Granting Administrator status to all new members.
- Not cleaning up old employees or inactive contributors.
- Not keeping an eye on security plugins that keep track of user actions.
- Not checking roles when growing your site (for example, installing WooCommerce).
Helpful Resources
Here are some resources for learning more about user roles and permissions:
- WordPress.org: Roles and Capabilities
- User Role Editor Plugin
- Members Plugin by MemberPress
- Wordfence Security Blog – for tips on securing user accounts
Conclusion
WordPress user roles and permissions management is not only a technical process- it’s the cornerstone of a well organised and secure website. By understanding what the five default roles are, how to customize them to your liking, and some best practices, you will be able to achieve the right balance for your site. Whether your site is a personal blog, an online store, or a large membership site, knowing your user roles will give you control over your workflows and your content. All things being equal, the better you can structure your user roles, which is yet another way to structure your site, the more professional and safer your site will be.
Another thing to remember is that WordPress sites evolve over time. As your team grows or new team members join or business needs evolve, your user roles also need to evolve. A configuration that was appropriate when you first launched your site may no longer be appropriate when you have a number of editors, SEO staff, or customer service representatives in the dashboard. Routinely reviewing and updating user roles keeps things in alignment and protects you from inappropriate exposure.
Finally, think of user roles as a part of your larger security strategy. Just like you would update plugins, monitor performance, or back up your content, role management requires ongoing attention. A couple of minutes spent granting users the right permissions today may save hours of headaches, or even greater security headaches tomorrow. When this habit becomes your investment, not only are you protecting your site, you are building a sustainable foundation for growth and success.
FAQs :
Can I create a custom WordPress user role?
Yes. WordPress roles can be customized using dedicated plugins or custom PHP code. This allows you to create permissions tailored to specific responsibilities, such as SEO, support, or content management.
What happens when I change a user’s WordPress role?
Changing a user’s role changes the capabilities available to that account. The user may gain access to additional WordPress features or lose permissions they previously had, depending on the new role.
Should every team member have an Administrator role?
No. Administrator access should generally be limited to people who genuinely need full control of the website. Giving unnecessary administrative access can increase the risk of accidental changes or security problems.
How often should WordPress user roles be reviewed?
User roles should be reviewed periodically, especially when employees leave, responsibilities change, or new plugins and services are introduced. Regular reviews help keep permissions aligned with current responsibilities.
What is the difference between a Contributor and an Author in WordPress?
An Author can write, edit, and publish their own posts, while a Contributor can write and edit their own posts but cannot publish them. Contributor content normally requires review before it goes live.